 ع


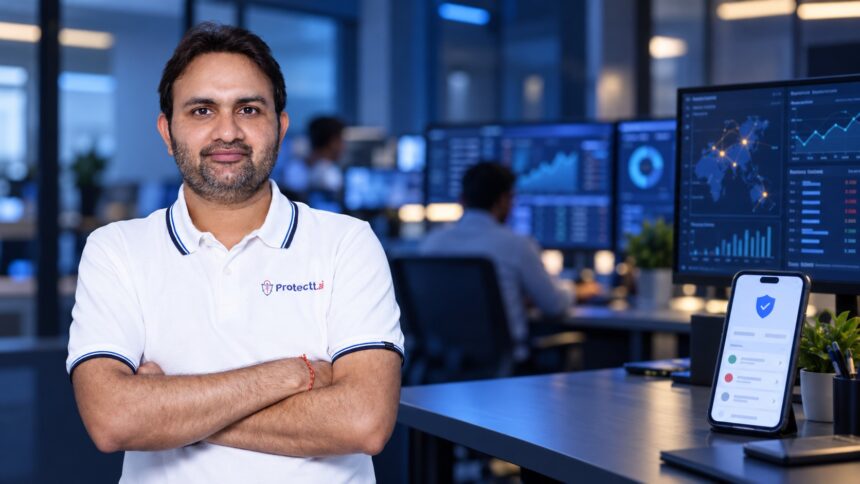
As digital payments become routine, convincing impersonation is complicating fraud prevention. Protectt.ai founder Manish Mimani argues that banks, fintechs and cybersecurity firms need a more coordinated response.
Saudi Arabia’s growing use of electronic payments illustrates what is at stake when fraud undermines confidence in digital finance. Cashless transactions are now an everyday habit, making the security of the people using payment systems as consequential as the reliability of the systems themselves.
The Saudi Central Bank reported in April that electronic payments represented 85% of retail payments in 2025, compared with 79% in 2024. Electronic transaction volumes across national payment systems reached 14.6 billion, up from 12.6 billion.
Those figures measure adoption, not fraud. But they provide the backdrop to a question facing financial institutions in Saudi Arabia and the UAE: how can customers distinguish legitimate requests from convincing imitations when artificial intelligence makes impersonation easier?
For Cybersecurity Awareness Month, Manish Mimani, founder and CEO of mobile application security company Protectt.ai, argues that the consequences extend beyond compromised accounts or interrupted services.
“The digital ambitions of the UAE and Saudi Arabia depend on people being able to trust the services they use every day,” he said in written commentary supplied for the occasion. “Cyber fraud puts that trust at risk, along with a family’s lifetime savings or a small business’s working capital.”
When familiar warning signs become less useful
Fraud awareness has often encouraged customers to question poorly written messages, unfamiliar senders and implausible requests. Generative AI complicates that approach by helping criminals produce more polished material and impersonate people through several forms of media.
A December 2024 warning from the FBI’s Internet Crime Complaint Center described criminals using AI-generated text, images, audio and video to support financial fraud. Its examples included fabricated identification documents, cloned voices and video calls involving supposed executives or other authority figures.
The agency also warned that AI can reduce the effort needed to deceive victims and correct mistakes that might otherwise expose a scam. Its warning documents methods rather than measuring their prevalence in either Gulf market.
“While consumer awareness and digital hygiene remain critical first lines of defense, the nature of fraud is rapidly changing,” Mimani said.
The distinction matters for public messaging. Awareness remains useful, but recognising suspicious content becomes a harder task when the content itself is increasingly convincing. A familiar voice or polished message cannot, by itself, establish who is behind a request.
Saudi controls already recognise the need to cooperate
Mimani’s call for closer cooperation has a clear parallel in Saudi Arabia’s existing regulatory approach.
Under SAMA’s Counter-Fraud Framework provisions on intelligence monitoring, member organisations should share information on emerging fraud methods and threats with the central bank and other organisations in the sector, where laws and contractual terms permit.
The provisions also address sharing login information associated with confirmed fraud cases through the Sectorial Anti-Fraud Committee, and analysing information received from other institutions to assess customers’ exposure.
That is a more specific task than exchanging general warnings. It involves turning an incident detected by one organisation into information another can use.
A separate set of Counter-Fraud Fundamental Requirements, effective from April 13, 2026, covers the finance sector, payment systems and payment service providers. It addresses investigation, identifying the causes of incidents and taking corrective action, including sharing relevant information where permitted.
Together, these measures show that cooperation is already part of the supervisory framework. Their existence does not establish how effectively every institution implements them, or how quickly an emerging threat becomes a working control.
“No single cybersecurity enterprise, banking institution, or fintech player can solve this crisis in isolation,” Mimani said.
The UAE’s parallel question: who oversees the AI?
The UAE has also addressed the responsibilities that accompany financial institutions’ own use of AI.
In an announcement dated February 23, 2026, the Central Bank of the UAE outlined guidance on responsible AI and machine learning use by licensed financial institutions. Its principles include accountability, fairness, transparency, explainability, human oversight and data privacy.
This concerns institutions’ deployment of the technology, rather than serving as a measurement of AI-enabled crime. It nevertheless introduces an important consideration into the response: systems used to protect customers also need oversight.
The implication for fraud prevention is that stronger detection cannot be assessed solely by how many transactions a system flags. A legitimate customer incorrectly blocked from making a payment also experiences a failure of service. Institutions must be able to examine decisions and resolve mistakes.
For banks and fintechs, this creates two related responsibilities: recognise increasingly convincing deception and ensure their own automated responses remain accountable to the people affected.
Turning a shared warning into measurable action
Mimani’s proposed response centres on analysing emerging threats, sharing intelligence and deploying updated defences across banking, financial services, insurance and cybersecurity.
The practical question is what happens after a threat is identified. Does the information reach the relevant fraud team? Can it change an institution’s controls? Is there a process for reviewing similar incidents elsewhere?
These are operational questions rather than claims that one technology can eliminate fraud. They also make the limits of the available evidence important. The Saudi payment figures demonstrate the scale of digital adoption, while the FBI warning explains criminal methods. Neither provides a comparable estimate of AI-related fraud losses across the UAE and Saudi Arabia.
Measuring progress therefore requires more than reports of increased technology spending. Relevant questions include whether repeat attacks are being prevented, whether customers can report incidents promptly, and whether lessons from investigations produce changes that can be checked.
For this year’s awareness month, the policy foundations give the discussion a concrete starting point. Saudi frameworks already address information sharing and corrective action; the UAE’s guidance addresses accountability in financial AI. The next test is how those principles work when a convincing fraudulent request reaches a customer.